Over the past year, Qilin, also known as Agenda and AgendaCrypt, has established itself as one of the most prominent ransomware operations in the threat landscape. Operating under a Ransomware-as-a-Service (RaaS) model, the group has demonstrated a steady evolution in both its malware capabilities and affiliate ecosystem, allowing it to target organizations across multiple sectors and geographies.
Qilin’s operations are supported by resilient infrastructure, including services associated with bulletproof hosting providers. This infrastructure powers the group’s Tor data leak site, which forms a key component of its double-extortion model by publicly naming victims and publishing stolen data to increase pressure during ransomware negotiations.
Qilin follows a largely opportunistic targeting strategy, showing little preference for specific industries or countries. Its victims span multiple sectors, including manufacturing, healthcare, technology, and professional services, with organizations across North America, Europe, and other regions appearing on its leak site.
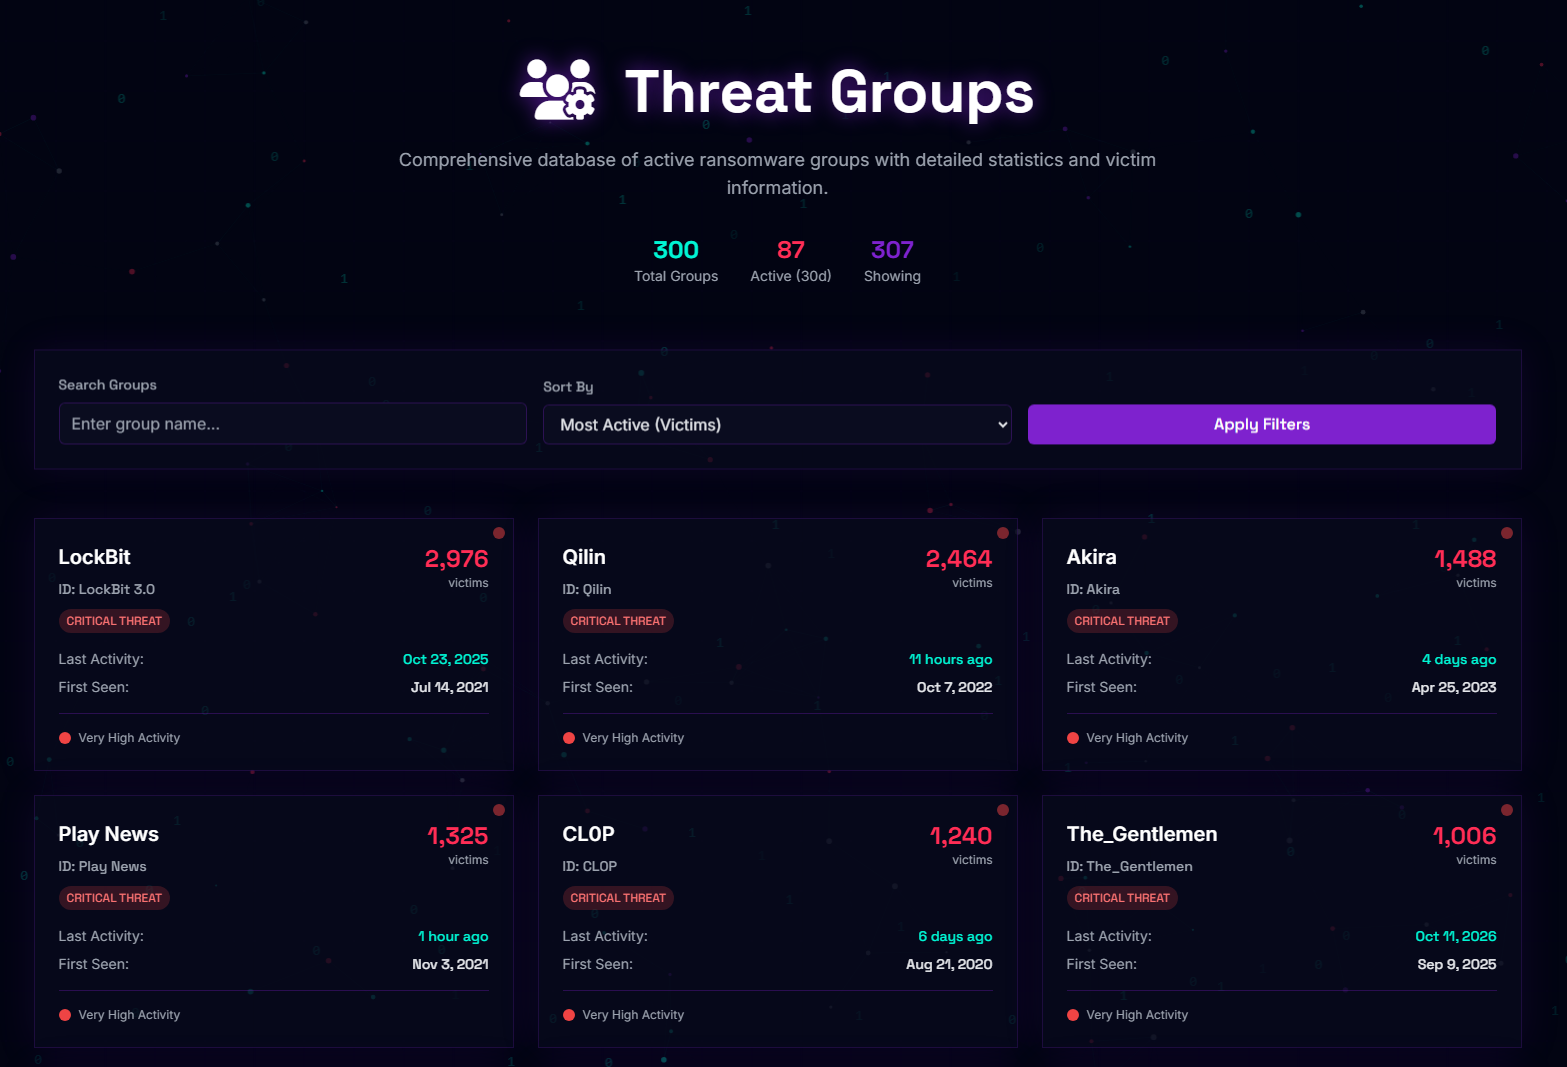
The wide range of affected industries and regions is also reflected in public ransomware tracking data. In fact, according to the Ransom-DB statistics, Qilin consistently ranks among the most active ransomware operations, recording a high volume of claimed victims compared to other major ransomware groups. This sustained activity highlights both the effectiveness of its affiliate ecosystem and its ability to maintain a steady stream of successful intrusions across diverse targets.
One notable aspect of Qilin’s evolution is the adoption of multiple platforms and programming languages. The ransomware is available in both Windows and Linux / ESXi variants and has evolved from its original Golang implementation toward a more recent Rust version. While both variants share the same core functionality, the Rust implementation has become increasingly prevalent in recent campaigns, likely due to its performance benefits and the additional challenges it presents to reverse engineers. Although Qilin actively targets both Windows and Linux/ESXi environments, this analysis primarily focuses on the Windows variant, as it is the version most commonly observed in real-world intrusions and provides the largest attack surface for enterprise environments.
Initial Access
The initial access techniques employed by Qilin affiliates have evolved over time. Historically, the group relied heavily on phishing campaigns, Business Email Compromise (BEC) operations, and the acquisition of valid credentials from Initial Access Brokers (IABs) to gain a foothold within victim environments.
More recently, however, Qilin operators and affiliates have increasingly shifted toward the exploitation of publicly disclosed vulnerabilities, particularly those affecting internet-facing appliances, VPN gateways, backup infrastructure, and enterprise management platforms.
Notable and recent vulnerabilities linked to Qilin intrusions include:
- CVE-2026-0257 - Palo Alto Networks PAN-OS / Prisma Access authentication bypass.
- CVE-2026-5075 - Check Point Remote Access & Mobile Access VPN authentication bypass.
- CVE-2026-20079 + CVE-2026-2036 - Cisco Secure Firewall Management Center (FMC) authentication bypass.
Windows Encryptor
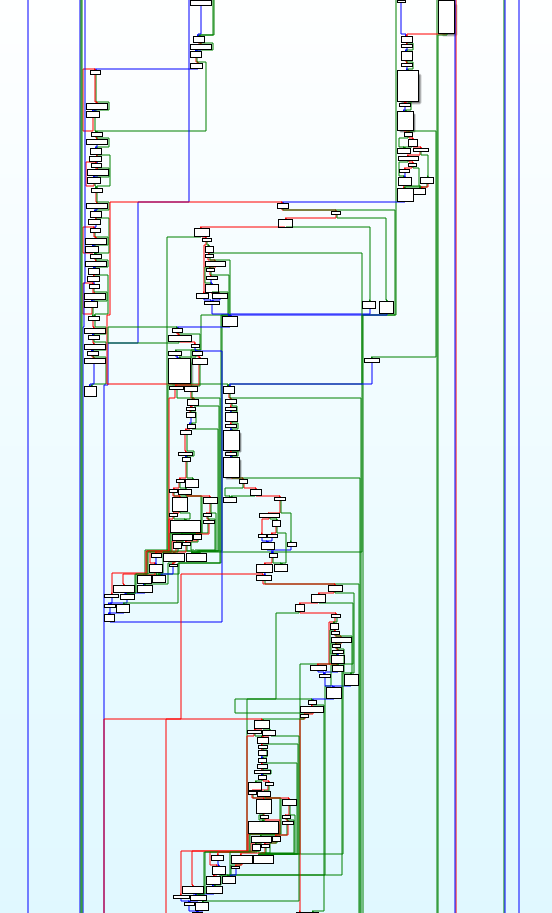
The Windows variant of Qilin is distributed as a 32-bit Portable Executable (PE), typically ranging between 2 and 4 MB in size. In many observed samples, the payload is compressed using the UPX packer, likely to reduce its size and complicate static analysis. Since the ransomware is written in Rust, execution does not immediately reach the ransomware logic; instead, the PE entry point traverses the standard MinGW startup routines before invoking the Rust main() function. Additionally, TLS callbacks are used to perform runtime initialization and cleanup tasks before and after the core ransomware functionality executes.
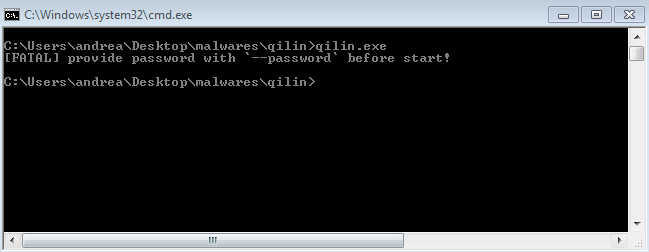
Qilin supports numerous command-line arguments that allow affiliates to customize its behavior during execution. Notably, the ransomware requires a password to be supplied through the --password parameter, which acts as a prerequisite for execution.
Beyond this requirement, operators can configure delayed execution (--timer), restrict encryption to specific paths or hosts (--paths, --ips), enable lateral movement across Windows, ESXi, and vCenter environments (--spread, --spread-vcenter), disable safety checks and anti-analysis features (--no-vm, --no-sandbox), suppress ransomware notes and visual artifacts (--no-note, --no-wallpaper), reboot systems into Safe Mode (--safe), destroy cluster environments (--kill-cluster), skip local or network encryption targets, archive operational logs, or perform a complete encryption simulation through a dedicated --dry-run mode.
Unfortunately, the use of Rust significantly complicates reverse engineering due to the large amount of compiler-generated code, complex control flow, and extensive runtime components embedded within the binary. As a result, distinguishing malicious functionality from legitimate runtime logic can be challenging and time-consuming. Therefore, rather than providing a function-by-function breakdown, this analysis focuses on the ransomware’s core capabilities and execution workflow.
Recovery Inhibition Routine
At the start of the main() function, the ransomware launches a separate thread for process and service interference. That thread handles processes first, then services. The main thread continues without waiting for it, so interference can overlap the delay and need not finish before encryption begins.
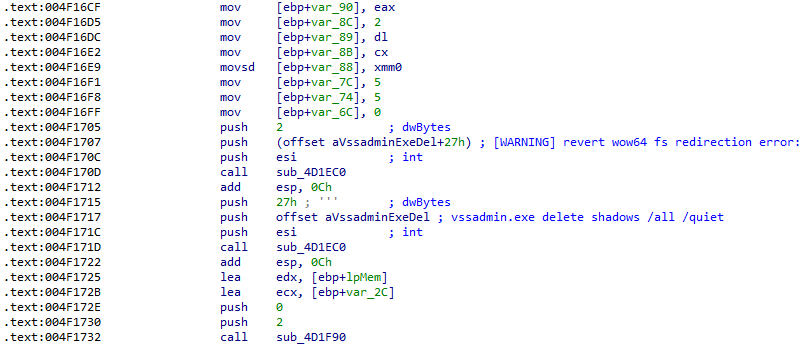
AFter setting up the thread, the launcher attempts to delete the shadow copies creating a recognizable child process through the command cmd.exe /C vssadmin.exe delete shadows /all /quiet. Additionally, on WOW64, the program attempts to disable filesystem redirection around that command. This is necessary because WOW64 transparently redirects access from C:\Windows\System32 to the 32-bit SysWOW64 directory, potentially causing the process to interact with 32-bit system components rather than the native 64-bit binaries. By disabling redirection, Qilin ensures that the legitimate 64-bit vssadmin.exe is executed successfully.
Processes and Services Termination
The separate interference thread handles processes before services, though either operation can fail or be delayed by the host.
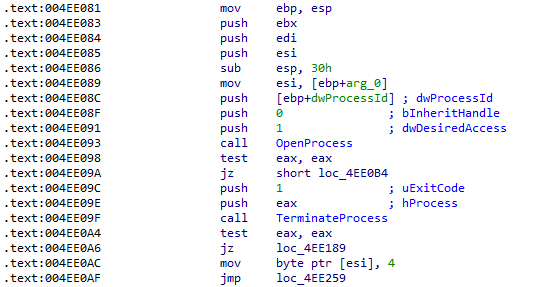
The process path call the EnumProcesses API with a fixed 16 KiB buffer. The resulting processes are matched through case-insensitive regular expressions against a predefined list of processes that could interfere with file encryption or maintain locks on valuable data. The target list includes productivity applications such as Microsoft Outlook, Microsoft Word, Excel, and PowerPoint, database-related processes such as Oracle, SQL Server, as well as virtualization and management components including Hyper-V. The matching processes are terminated with a call to the TerminateProcess API with the PROCESS_TERMINATE flag.
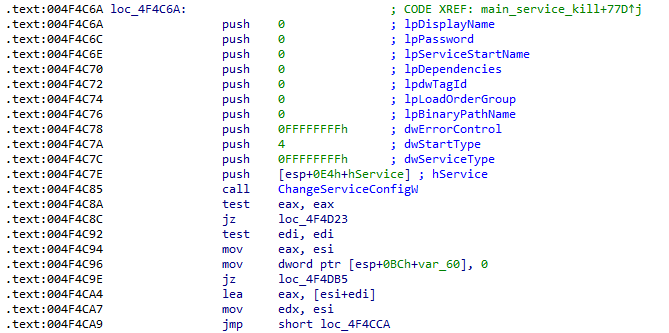
In addition to processes, Qilin also tries to terminate a predefined list of Windows services primarly associated to backup solutions, database platforms, email infrastructure, and enterprise applications, including Veeam, Acronis, Microsoft Exchange, SQL Server, SAP, and Commvault components. The service inventory call the EnumServicesStatusW API and, similarly to the process inventory, matches the desired services through case-insensitive regular expressions. The matching services are teminated with a call to the ChangeServiceConfigW API with the SERVICE_DISABLED flag.
Storage Discovery
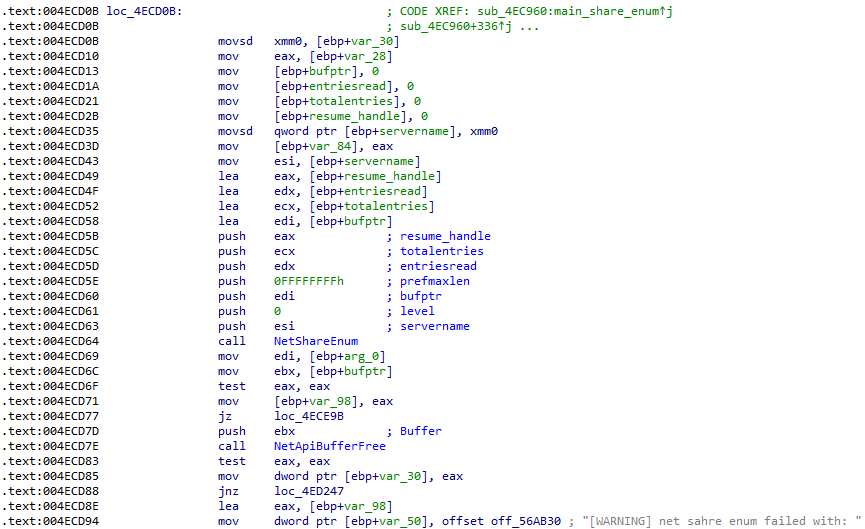
When explicit paths or hosts are supplied through the command-line parameters, the encryptor foillows those targets. Otherwise, Qilin enumerates both local and remote storage resources to maximize the impact of the encryption process. For local storage discovery, the ransomware leverages the GetLogicalDrives API, which returns a bitmask representing all logical drives currently accessible on the system, including fixed disks, removable media, and mapped drives. In parallel, Qilin uses the NetShareEnum API to enumerate network shares exposed by remote systems, allowing it to identify additional storage locations that may be accessible through the compromised user context.
To maximize encryption coverage while preserving system stability, Qilin implements multiple layers of filtering based on file extensions, directory names, and specific filenames. The ransomware excludes a large number of extensions associated with operating system components and executables, such as .dll, .exe, .sys, .drv, .msi, .bat, and .cmd, preventing the accidental corruption of files required for continued execution of Windows and the ransomware itself. Additionally, the ransomware skips critical operating system locations such as Windows, System Volume Information, Boot, Program Files, Program Files (x86), ProgramData, AppData, SysVol, and NetLogon, as well as directories related to browsers and common applications. Likewise, it excludes important system files including bootmgr, ntldr, boot.ini, ntuser.dat, desktop.ini, and thumbs.db.
Encryption Routine
Like most modern ransomware families, Qilin implements a hybrid encryption scheme that combines the speed of symmetric cryptography with the secure key management provided by asymmetric cryptography. Specifically, the ransomware leverages ChaCha20 to encrypt victim files and RSA to protect the encryption material required for recovery.
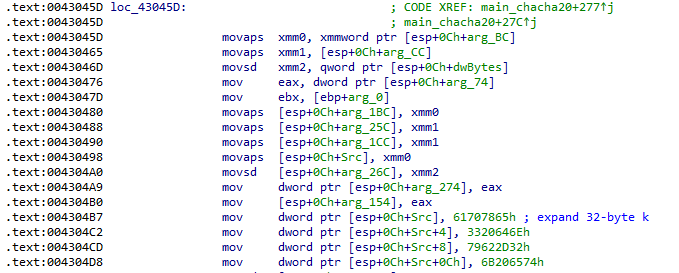
The encryptor uses standard 20-round ChaCha20. Its state constants decode to expand 32-byte k, and the round function uses the 16/12/8/7 rotation schedule. To ensure randomness for each encrypted file, Qilin generates a unique ChaCha20 key and nonce through a thread-local CSPRNG (Cryptographically Secure Pseudo-Random Number Generator) with a 32 bytes seded from the BCryptGenRandom API.
Since ChaCha20 is a symmetric algorithm, the same key required to encrypt the file is also required to decrypt it. Simply storing this key alongside the encrypted data would allow defenders to recover the file without interacting with the attackers. To prevent this, Qilin encrypts the ChaCha20 key material using an embedded RSA public key and appends the resulting encrypted blob to the end of the encrypted file together with other metadata.
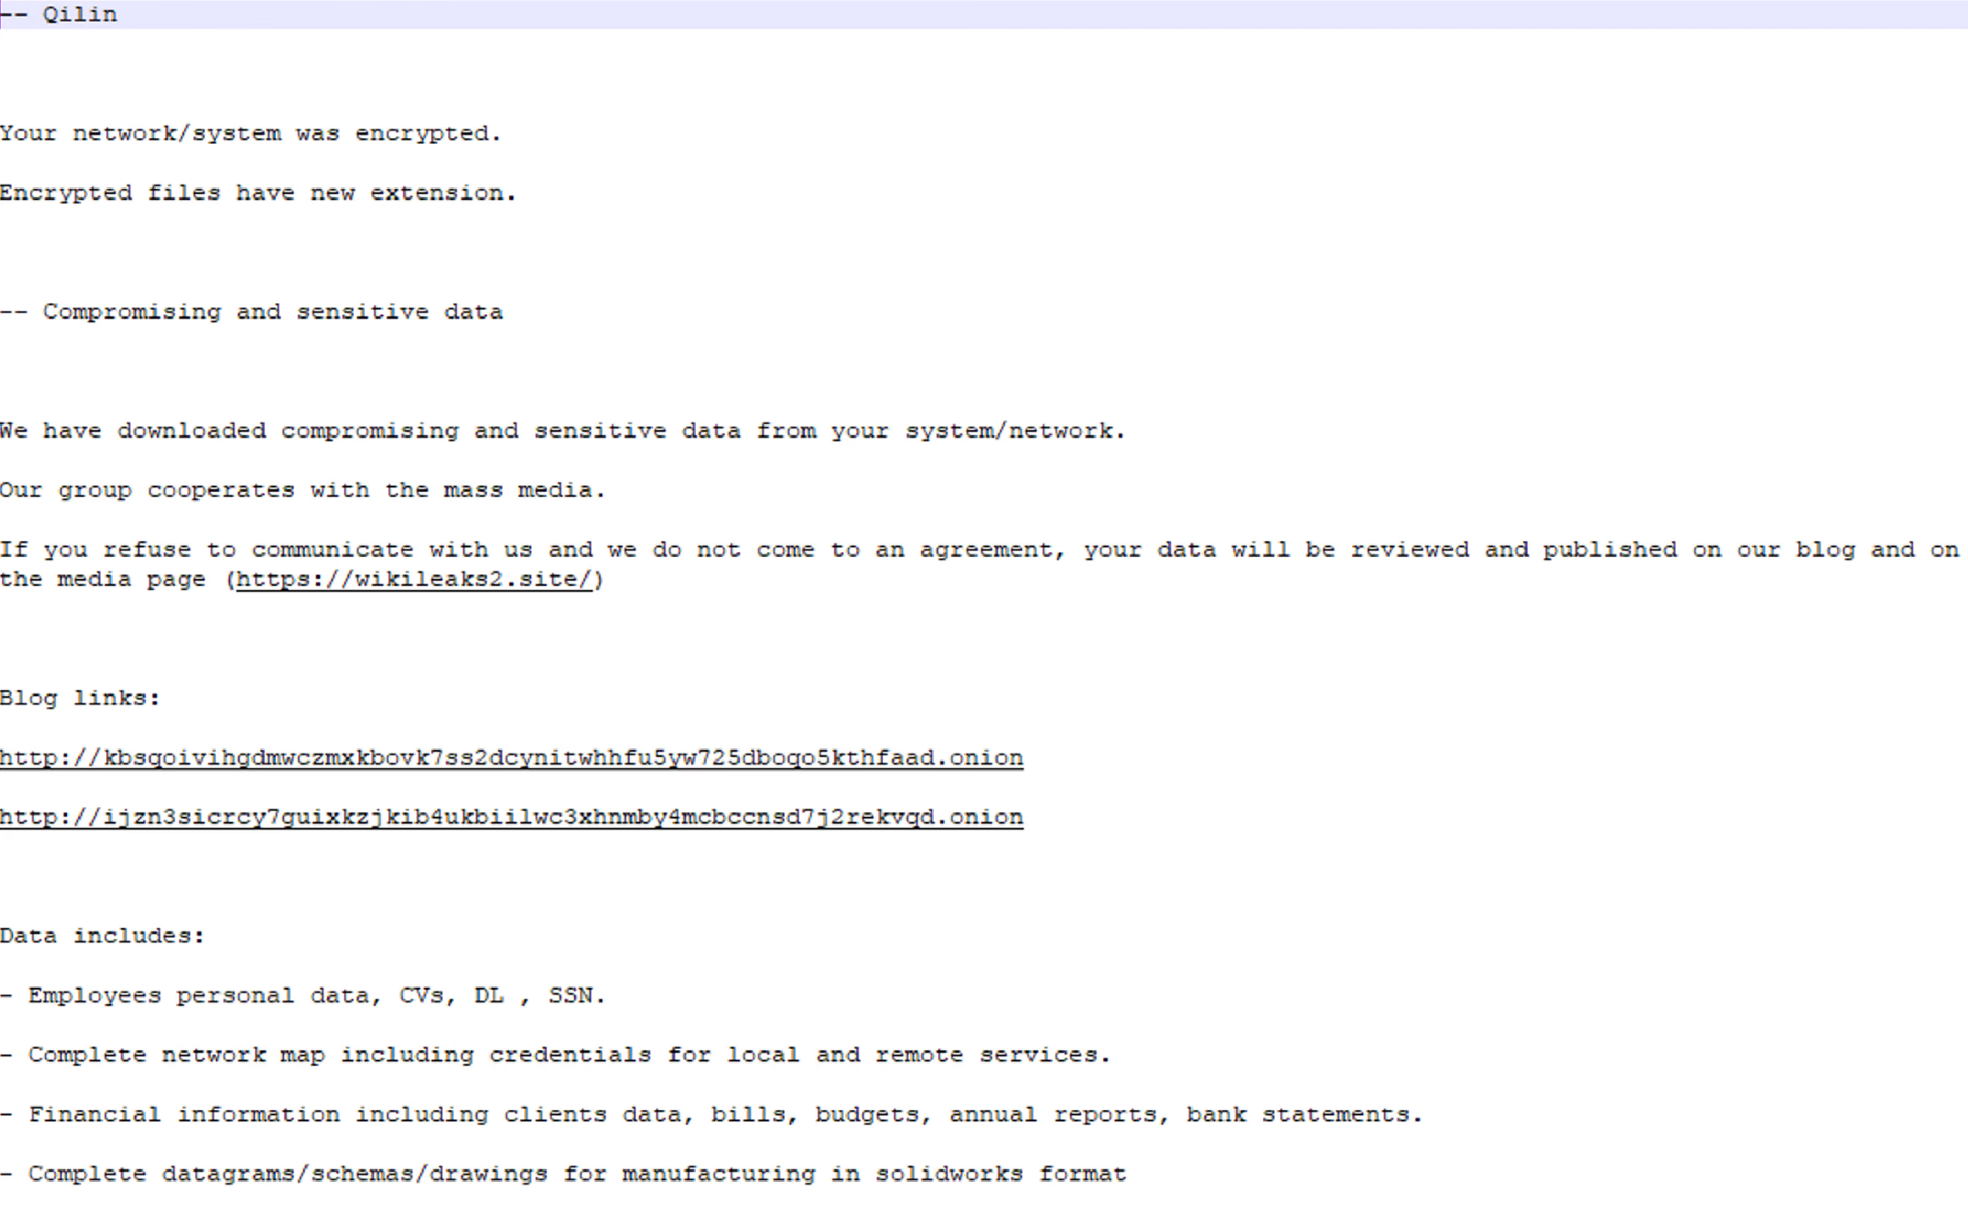
Upon successfull encryption, the ransomware adds a per-victim / per-campaign extension to the encrypted files and, for each directory, drops the ransomware note (usually named README-RECOVER-*.txt) containing victim-specific information and payment instructions for accessing the operators TOR-based negotiation portal.
Detection Opportunities
From a detection perspective, YARA rules remain one of the most effective mechanisms for identifying Qilin samples, particularly during static analysis. Despite the use of Rust and, in some cases, UPX packing, many samples contain highly distinctive strings that are rarely encountered in legitimate software. Examples include debug and error messages such as [FATAL] provide password with --password before start, operational artifacts like vssadmin.exe delete shadows /all /quiet, and Rust source-code paths embedded in the binary, including encryptor/src/config/embedded_config.rs and /usr/src/myapp/file_encryption/src/lib.rs.
rule MALWARE_Win_Qilin {
	meta:
		author = "Andrea Naspi"
		date = "2026-10-28"
		description = "Detects the Qilin Rust-based Windows encryptor and decryptor"
		tlp = "green"
		version = "1.0"
		id = "845f6412-c1a3-42c9-861c-6a6625881693"
		hash = "37546b811e369547c8bd631fa4399730d3bdaff635e744d83632b74f44f56cf6"
		hash = "f910b2a6d84d0677cda9aefabfa4a45863ba51a8831588e3b527e8e1d3a9927c"
		packed_hash = "650a03c40c45eef3590058c37de8ea2e978c9c69f289390b2ab89be3910549fb"

	strings:
		// Rust-based artifacts
		$rust_1 = "RUST_BACKTRACE" ascii
		$rust_2 = "Local\\RustBacktraceMutex" ascii
		// Rust source code paths
		$path_1 = "/usr/src/myapp/file_encryption/src/lib.rs" ascii
		$path_2 = "/usr/src/myapp/rsa/src/oaep.rs" ascii
		$path_3 = "decryptor/src/pipelines/decryption_pipeline.rs" ascii
		// Operational artifacts
		$cmd = "vssadmin.exe delete shadows /all /quiet" ascii
		// Debug-related strings
		$debug_1 = "provide password with `--password` before start" ascii
		$debug_2 = "Cannot parse public key" ascii
		$debug_3 = "45 seconds before encrypt" ascii
		$debug_4 = "Waiting for all encryption jobs to complete" ascii
		$debug_5 = "File was encrypted with ChaCha20" ascii
		$debug_6 = "File was encrypted with AES-CTR" ascii


	condition:
		uint16(0) == 0x5A4D and
		uint32(uint32(0x3c)) == 0x00004550 and
		filesize <= 10MB and
		any of ($rust_*) and
		(
			any of ($path_*) or
			$cmd
		) and
		2 of ($debug_*)
}
Because Qilin samples are frequently distributed in a UPX-packed form, static detection alone may not always be sufficient, particularly when adversaries modify or repackage the payload. For this reason, host-based telemetry should complement signature-based detection strategies. Behavioral indicators such as the deletion of the shadow copies, the termination of backup and database services, mass file modifications, and the creation of ransomware notes can provide high-fidelity detection opportunities.
title: Qilin ransomware - shadow copies deletion
id: 27ab652e-909d-486f-966a-f9d7460e3c78
status: experimental
description: Detects the usage of vssadmin.exe to delete the shadow copies
author: Andrea Naspi
date: 2026-10-28
logsource:
  product: windows
  category: process_creation
detection:
	selection_img:
		Image|endswith:
			- '\powershell.exe'
			- '\cmd.exe'
			- '\wmic.exe'
			- '\vssadmin.exe'
			- '\diskshadow.exe'
	selection_cli:
		CommandLine|contains|all:
			- 'shadow'
			- 'delete'
  condition: selection_img and selection_cli
level: high
falsepositives:
  - Legitimate administrator deletes Shadow Copies using operating systems utilities for legitimate reason
tags:
  - tlp.green
  - attack.impact
  - attack.t1490